How to Spot Domain Renewal Scam Emails and Fake Invoices?
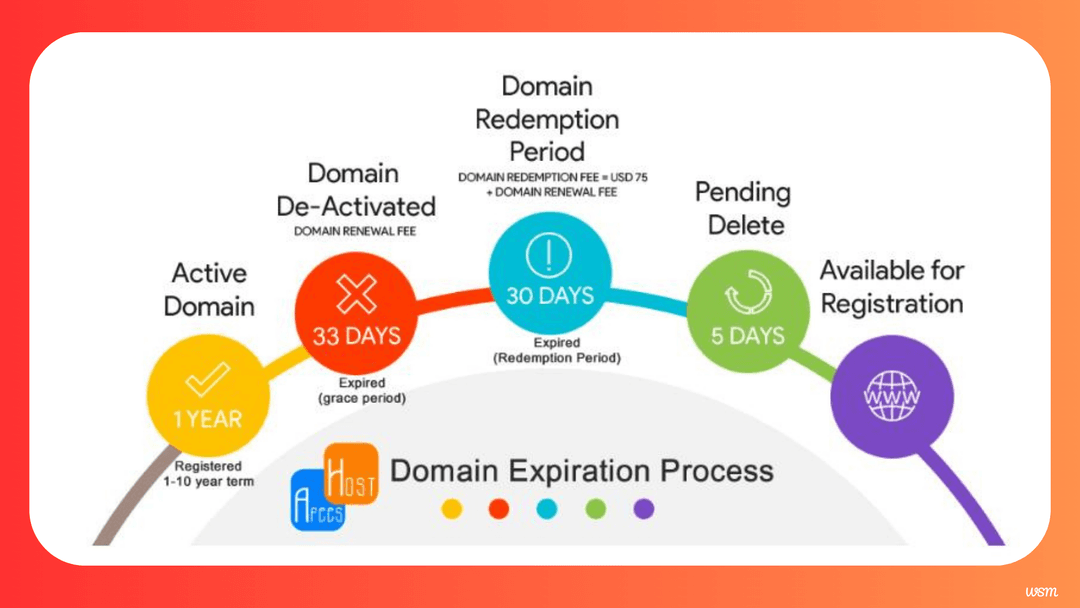
Register a domain and, within days, the mail starts arriving: "Final notice: your domain is about to expire", "Domain listing invoice", "Urgent: another company wants to register your brand in Asia". Some of these are genuine reminders from your registrar. Many are not. Domain renewal scams are one of the oldest tricks on the internet because domain contact details have historically been public, renewal deadlines are real, and the consequences of letting a domain lapse are scary. This guide explains the common types of renewal scams, the red flags that give them away, how to verify a notice in under a minute using WHOIS or RDAP, how to check an email's authentication headers, and what to do if you have already paid or clicked. If you want to understand what genuinely happens when a domain expires, read about the domain expiration process first, because knowing the real timeline is the best defense against fake urgency.
Why Domain Owners Are Targeted
Three things make domain owners attractive targets:
- Contact data is discoverable. Before privacy services and GDPR-era redaction, WHOIS published registrant names, postal addresses, emails, and phone numbers. Scammers harvested these in bulk, and old lists still circulate. Even today, newly registered domains are easy to enumerate from zone files and certificate transparency logs.
- Expiration dates are public. WHOIS and RDAP show when a domain expires, so scammers can time their notices to arrive just before the real deadline.
- The stakes feel high. Losing a domain can take down a website and email. Fear of that outcome pushes people to pay first and check later.
Using a WHOIS privacy protection service reduces, but does not eliminate, this exposure.
The Most Common Renewal Scams
1. Domain Slamming (Fake Renewal That Is Really a Transfer)
Slamming is a letter or email that looks like a renewal invoice but is actually a solicitation to transfer your domain to a different registrar, usually at a much higher price. The fine print often says something like "this is not a bill" or "by returning this notice you authorize the transfer of your domain". If you pay, you may end up moving your domain to a company you never chose, often with worse service and higher renewal fees.
Slamming has historically arrived by postal mail on official-looking paper with payment slips. In the United States, the Federal Trade Commission took action against a company over this practice in the early 2000s, but similar letters keep appearing from different senders.
2. Phishing "Your Domain Has Expired" Emails
These emails imitate your registrar or a generic "domain services" brand and include a link to "renew now". The link goes to a lookalike login page that steals your registrar username, password, and sometimes your one-time code. With registrar access, an attacker can change name servers, unlock the domain, and transfer it away. This is one of the main routes to domain hijacking.
Some versions skip the login page and go straight to a card payment form, so the scammer collects card details instead of, or as well as, credentials.
3. "Search Engine Registration" or "Domain Listing" Invoices
These look like an invoice for your domain, mention your domain name and its expiration date prominently, and ask for an annual fee. Read carefully and you will find the service is "search engine submission", "web listing", or "SEO optimization" with no relationship to your registration. Paying does nothing for your domain, and the service is typically worthless. Search engines do not charge to be included in their index.
4. The "Asian Domain Registration" Scam
You receive an email from a supposed registrar in another country saying a company has applied to register your brand name under several country-code TLDs or as an "internet keyword", and asking whether you authorize it. The aim is to scare you into buying a bundle of overpriced domains to "protect" your brand. There is usually no other applicant. Genuine registrars do not contact trademark owners to ask permission before registering a domain for a customer.
5. Fake Payment Failure Notices
"Your auto-renewal payment failed. Update your card within 24 hours or your domain will be deleted." These mimic billing systems and lead to a card-harvesting page. They are especially convincing if you really do use auto-renewal.
6. Fake ICANN or Registry Notices
Emails claiming to be from ICANN, Verisign, or "the domain registry" demanding payment or verification. ICANN does not sell domains, does not bill registrants, and does not send renewal invoices. Registries generally do not deal with registrants directly either; your registrar does.
Genuine Notices You Should Expect
Not every email about your domain is a scam. Knowing what legitimate notices look like helps you tell them apart.
| Legitimate notice | Who sends it | What it asks for |
|---|---|---|
| Expiration reminders | Your registrar | Renew through your existing account |
| Post-expiration notice | Your registrar | Renew or restore before the domain is deleted |
| WHOIS data reminder | Your registrar | Review your contact details, usually yearly |
| Registrant contact verification | Your registrar | Click a link to confirm your email after registration or a contact change |
| Transfer authorization or confirmation | Your registrar | Approve or confirm a transfer you initiated |
For gTLDs, ICANN's Expired Registration Recovery Policy (ERRP) requires registrars to send renewal reminders at set intervals, roughly one month and one week before expiration, and another notice shortly after expiration. ICANN's WHOIS Data Reminder Policy (WDRP) requires an annual reminder to review your contact data. Both come from your registrar, and neither asks you to pay anyone else.
Red Flags That Give a Scam Away
Run through this checklist whenever a renewal notice arrives:
- The sender is not your registrar. If you registered with Registrar A, a notice from Company B is not a renewal. It is a sales pitch or a scam.
- The expiration date is wrong. Scammers often use stale or estimated dates.
- The price is unusually high compared with what you paid last time.
- Fine print mentions "transfer", "solicitation", "not a bill", "listing", or "SEO".
- Extreme urgency: "within 24 hours", "final notice", "your domain will be deleted today". Real expiration involves grace and redemption periods, explained in domain grace period and redemption period.
- Links that do not point to your registrar's real domain, or that use lookalike spellings.
- Requests for unusual payment methods, such as wire transfer, gift cards, or cryptocurrency.
- Generic greetings like "Dear domain owner" rather than your account name.
- Postal mail invoices for domains you manage entirely online.
- Requests for your password or one-time code by email or phone. No legitimate registrar asks for these.
How to Verify a Notice in Under a Minute
The golden rule: never act from the email itself. Instead, verify independently.
Step 1: Look Up the Real Registrar and Expiration Date
Use WHOIS:
whois example.com | grep -iE "registrar:|expir"
Or use RDAP, which returns structured data that is easier to parse:
curl -sL https://rdap.org/domain/example.com \
  | jq -r '.events[] | select(.eventAction == "expiration") | .eventDate'
If the notice names a different company than the registrar shown here, or a different expiration date, you have your answer. For more background on these lookups, see what RDAP is.
Step 2: Log In Directly
Type your registrar's address into the browser yourself, or use a bookmark, and log in. If a renewal really is due, your dashboard will show it. If your account shows the domain is fine, the email was fake.
Step 3: Check the Email's Authentication Results
Most mail providers record SPF, DKIM, and DMARC results in the Authentication-Results header. In Gmail, use "Show original"; in Outlook, "View message source". Look for lines like this:
Authentication-Results: mx.example.net;
       dkim=pass header.d=real-registrar.com;
       spf=pass smtp.mailfrom=real-registrar.com;
       dmarc=pass header.from=real-registrar.com
A pass only proves the email came from the domain shown, not that the domain is trustworthy. A scammer can pass DMARC for domain-renewal-services.net. What matters is that the authenticated domain matches your registrar's real domain. A dmarc=fail on a message claiming to be from your registrar is a strong warning sign. If authentication records are unfamiliar, what a DMARC record is explains how these checks work.
Step 4: Automate the Check
If you manage many domains, this Python script reads a saved email (.eml), extracts the sender domain and authentication results, finds any domain names mentioned in the subject, and compares the claimed expiration context against RDAP. It uses only the standard library.
import email
import email.utils
import json
import re
import sys
import urllib.request
from email import policy

MY_REGISTRAR_DOMAINS = {"real-registrar.com"}  # your registrar's sending domains
MY_DOMAINS = {"example.com", "example.org"}    # domains you own


def rdap_info(domain):
    req = urllib.request.Request(
        f"https://rdap.org/domain/{domain}",
        headers={"Accept": "application/rdap+json"},
    )
    with urllib.request.urlopen(req, timeout=20) as resp:
        data = json.load(resp)
    expiry = next(
        (e["eventDate"] for e in data.get("events", []) if e["eventAction"] == "expiration"),
        "unknown",
    )
    registrar = "unknown"
    for ent in data.get("entities", []):
        if "registrar" in ent.get("roles", []):
            for prop in ent.get("vcardArray", [None, []])[1]:
                if prop[0] == "fn":
                    registrar = prop[3]
    return registrar, expiry


with open(sys.argv[1], "rb") as fh:
    msg = email.message_from_binary_file(fh, policy=policy.default)

from_addr = email.utils.parseaddr(msg["From"])[1]
sender_domain = from_addr.rsplit("@", 1)[-1].lower()
auth = str(msg.get("Authentication-Results", ""))
dmarc = re.search(r"dmarc=(\w+)", auth)

print(f"From:   {from_addr}")
print(f"DMARC:  {dmarc.group(1) if dmarc else 'not found'}")
if sender_domain not in MY_REGISTRAR_DOMAINS:
    print(f"WARNING: {sender_domain} is not one of your registrar's domains")

body = msg.get_body(preferencelist=("plain", "html"))
text = f"{msg['Subject']} {body.get_content() if body else ''}".lower()
for domain in MY_DOMAINS:
    if domain in text:
        registrar, expiry = rdap_info(domain)
        print(f"{domain}: real registrar = {registrar}, real expiry = {expiry}")
Run it with python3 check_notice.py suspicious.eml. It will not catch every scam, but it quickly surfaces the two facts that expose most of them: who really sent the message and whether the domain is actually close to expiring.
Prevent the Problem in the First Place
The easiest way to make renewal scams harmless is to remove the uncertainty they exploit.
- Turn on auto-renewal for every domain you want to keep, and keep a valid backup payment method on file. See how to set up domain auto-renewal.
- Register for multiple years for important domains, so a renewal notice is rarely legitimate.
- Consolidate domains at one or two registrars you trust, so any other sender is immediately suspicious.
- Use a dedicated email address for registrar accounts, ideally on a domain you control, and filter messages from your registrar's real domains into a trusted folder.
- Enable strong two-factor authentication on registrar accounts, preferably a security key, so stolen passwords are not enough.
- Keep registrar lock on, so even a compromised account cannot instantly transfer domains away.
- Maintain a domain inventory with registrar, expiry date, and renewal status, and review it quarterly.
- Train whoever handles invoices. Accounts payable teams are a common target for postal slamming letters.
What to Do If You Already Clicked or Paid
Act quickly and in this order:
- If you entered your registrar password, log in from a known-good link and change it immediately. Revoke active sessions, rotate API keys, and re-check two-factor settings.
- Check your domains: confirm name servers, contact emails, and lock status have not changed. Re-enable registrar lock if it was removed.
- If you entered card details, contact your bank or card issuer to block the card and dispute the charge.
- If you authorized a transfer by mistake, contact your current registrar right away. For gTLDs, a pending transfer can often be stopped before it completes, and ICANN's Transfer Policy provides a dispute route for transfers you did not intend.
- Report the scam. Forward phishing to your registrar's abuse team and to the impersonated brand. In the US you can report fraud to the FTC; most countries have an equivalent consumer protection or cybercrime agency. Reporting the sending domain's abuse contact helps get it suspended.
- Watch for follow-ups. Once a scam works, the same group may try again with a new pretext.
Domain Renewal Scams FAQ
Run a WHOIS or RDAP lookup on the domain. The Registrar field shows the accredited registrar that currently manages the registration. Any renewal notice from a different company is not a genuine renewal.
Usually not. Most registrars communicate only by email and through their dashboards. Postal renewal letters from unfamiliar companies are often slamming attempts that transfer your domain to them if you pay.
No. ICANN coordinates the domain system and accredits registrars but does not sell domains or bill registrants. Any invoice claiming to come from ICANN is fraudulent.
Almost certainly not. This is a long-running scam designed to pressure you into buying overpriced domains. Real registrars do not ask trademark owners for permission before processing a customer's registration.
No. For most gTLDs there is a renewal grace period after expiration, followed by a redemption period, before the domain is released. The exact durations depend on the registry and registrar, but deletion is not instant.
Yes. Scammers can authenticate mail from their own domains. Authentication only proves which domain sent the message, so always check that the authenticated domain matches your real registrar.
Contact your bank or card issuer to dispute the charge, keep copies of the invoice and correspondence, report it to your national consumer protection agency, and verify your actual domain status directly with your registrar.
Conclusion
Domain renewal scams work because they borrow the shape of something real: domains do expire, registrars do send reminders, and losing a domain does hurt. The defense is to rely on facts you can verify yourself rather than on the message in front of you. Check who your registrar really is, check the real expiry date, log in directly, and look at the email's authentication results before you click or pay anything.
Combine that habit with auto-renewal, multi-year registrations, consolidated registrar accounts, and strong two-factor authentication, and most renewal scams become easy to ignore. When one does slip through, moving quickly to secure your account, lock your domains, and dispute payments will usually limit the damage.
Here are some useful references for going deeper on domain renewal scams and legitimate notices:
- ICANN: Expired Registration Recovery Policy — the rules for the renewal reminders registrars must send for gTLDs.
- ICANN: WHOIS Data Reminder Policy — why you receive an annual email asking you to review your contact details.
- ICANN: Registrant Benefits and Responsibilities — what registrants are entitled to from their registrar.
- CISA: Recognize and Report Phishing — general guidance on spotting and reporting phishing messages.
- RFC 7489: Domain-based Message Authentication, Reporting, and Conformance (DMARC) — the specification behind the DMARC results shown in email headers.